

#   #  ###  ####  ####  #   # #   #  ###  ####  #####        ###  #####
#   # #   # #   # #   # #   # ## ## #   # #   # #           #   # #
#   # #   # #   # #   #  # #  # # # #   # #   # #               # #
##### ##### ####  ####    #   #   # #   # #   # ####  #####    #  ####
#   # #   # #     #       #   #   # #   # #   # #             #       #
#   # #   # #     #       #   #   # #   # #   # #            #    #   #
#   # #   # #     #       #   #   #  ###  ####  #####       #####  ###
[ 0.000 ] happymode-25 kernel v6.6.0-hardened loading...
[ 0.014 ] cpu: x86_64  microcode: 0x2f  smep: on  smap: on  kaslr: on
[ 0.061 ] memory: wiping previous session residue.......... ok
[ 0.118 ] mount /dev/vault -> /home  (luks2, argon2id)     ok
[ 0.240 ] sysctl: kernel.kptr_restrict=2                   ok
[ 0.241 ] sysctl: kernel.dmesg_restrict=1                  ok
[ 0.242 ] sysctl: net.ipv4.tcp_syncookies=1                ok
[ 0.310 ] nftables: default policy DROP (ingress/egress)   ok
[ 0.402 ] apparmor: enforcing  37 profiles                 ok
[ 0.511 ] aslr: full  (randomize_va_space=2)               ok
[ 0.640 ] audit chain: hash-chained, tamper-evident        ok
[ 0.777 ] egress broker: fail-closed, policy loaded        ok
[ 1.000 ] boot attestation verified
[ 1.001 ] all systems nominal
[ 1.002 ] ACCESS GRANTED
girishbenni@happymode-25:~$ whoami
girishbenni

girishbenni@happymode-25:~$ cat about.txt
Security-focused builder. I write things that fail closed rather than fail
quietly.

Most of my work sits at the seam between an AI agent and the network it is
allowed to talk to, or between a Linux distribution and the assumptions it makes
about its own integrity.

I care about the boring parts: what happens on the bad path, whether the audit
log can be rewritten after the fact, whether a test can pass against the wrong
artifact. If a system cannot prove it is working, I do not count it as working.girishbenni@happymode-25:~$ ./skills --report
LANGUAGE PROFICIENCY
---------------------------------------------------------------
Python |###################### | 78%
Bash |##################### | 74%
Rust |############# | 44%
TypeScript |############ | 40%
PowerShell |########## | 34%
C / kernel |######## | 28%
DOMAIN FOCUS
---------------------------------------------------------------
Security engineering |########################## | 90%
Linux / OS plumbing |####################### | 82%
Networking |##################### | 74%
CI / build systems |################### | 66%
AI agent infrastructure |################### | 66%
Frontend |########## | 34%
POSTURE
---------------------------------------------------------------
default policy : DROP
secrets in repo : none
dependencies shipped : zero where avoidable
telemetry : off
🏆 trophy case
🧊 3D contribution graph
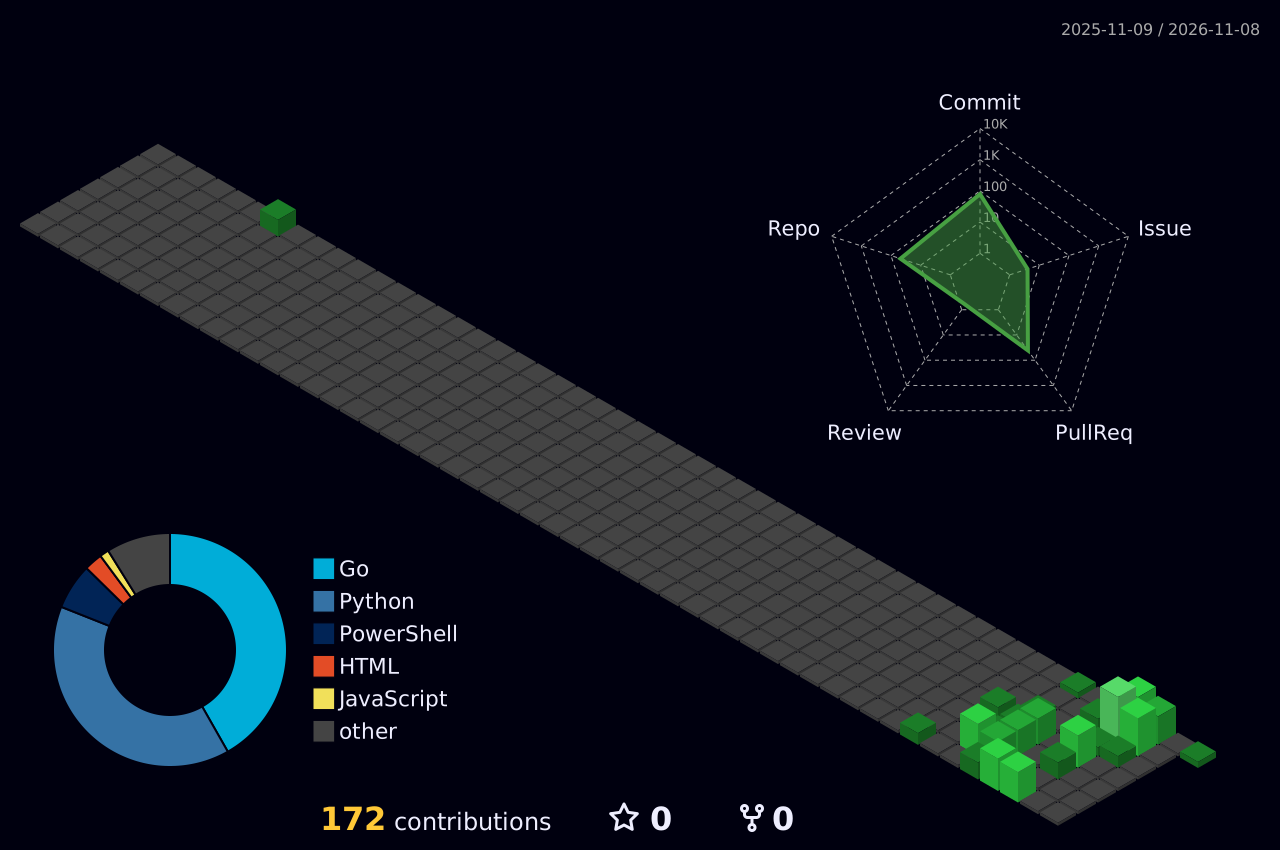
girishbenni@happymode-25:~$ ls -la ~/projects| project | description |
|---|---|
| network-mapper | Network service discovery and vulnerability assessment. FastAPI + asyncio scanner, React dashboard. |
| n8n-learner-hub | Automation learning hub built around n8n workflows. |
drwxr-xr-x  egress-broker/       fail-closed AI agent egress proxy
drwxr-xr-x  obsidian-os/         hardened Windows-feel Linux distribution
the two directories above are private, so they do not link. ask me for access.
A Windows-feel Linux, hardened by default. Custom distribution whose desktop mirrors Windows 11 conventions, paired with a unified Bash/PowerShell shell.
- five flavors, each a single package list:
dailydeveloperpentesterserverghost - CIS Debian Benchmark hardening, attested at boot
- hybrid BIOS + UEFI ISO built by mmdebstrap -> packages -> overlays -> squashfs
- boot test asserts on a marker stock Debian cannot emit
Status, stated plainly: the desktop does not exist yet. No window manager, no panel, no applications. Treat the Windows 11 look as a Phase 2 deliverable. An earlier claim of Phase 0 completion was wrong and is documented with evidence in the repo.
Fail-closed egress proxy for an AI agent. One file, Python 3.9+ standard library, no dependencies.
- DNS pinning, so resolution cannot drift under you
- threshold alerting, trips before a leak becomes a breach
- per-client policy scoping
- hash-chained, tamper-evident sqlite audit log






girishbenni@happymode-25:~$ ./connect --list
  github      https://github.com/happymode-25
  repos       https://github.com/happymode-25?tab=repositories
  linkedin    (not configured)
  twitter     (not configured)
  site        (not configured)
🔓 unauthorized access attempt
$ ssh root@happymode-25
root@happymode-25: Permission denied (publickey).

$ nmap -p- happymode-25
Starting Nmap 7.95
Note: host seems firewalled. all 65535 ports filtered.

$ curl -X POST https://happymode-25/override
{"error":"fail-closed","detail":"no such thing as fail-open","status":403}

$ echo "please let me in"
bash: this is not a negotiation
  +------------------------------------------+
  |  nice try.                               |
  |                                          |
  |  the audit log now contains your IP.     |
  |  the hash chain has been updated.        |
  |                                          |
  |  this is not a threat. it is a receipt.  |
  +------------------------------------------+